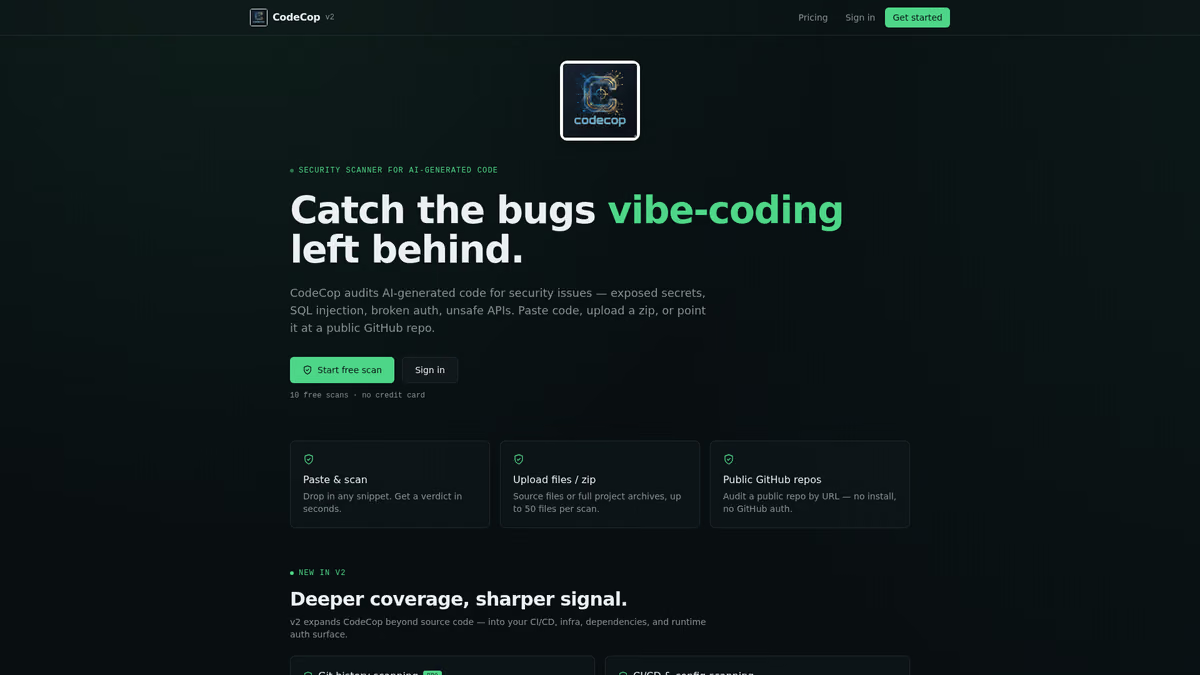
CodeCop audits AI-generated code for security issues like exposed secrets, SQL injection, broken auth and unsafe APIs, scanning pasted snippets, zipped projects (up to 50 files) or public GitHub repos with no install. The v2 pricing adds git history scanning (last 30 commits), CI/CD and infrastructure config checks (Dockerfiles, GitHub Actions, Terraform), cookie-flag checks, and CVE lookups against the OSV database with confidence-scored findings. It's pay-once with bring-your-own-key, and offers 10 free scans with no credit card.
What holds up
- +Pay once with your own API key — no recurring subscription for the scanning itself.
- +Checks real CVEs against the OSV database, not just generic pattern warnings.
- +Scans public GitHub repos directly by URL, with no install or GitHub auth needed.
Mind the limits
- −Git history scanning and some v2 checks are gated behind the Pro tier.
- −Zip/file uploads cap at 50 files per scan — larger projects need splitting.
Picked here? Add the badge
Put it on your site. It links back to this page. Free for every listed product.
<a href="https://stillworks.dev/products/p/codecop/"><img src="https://stillworks.dev/badge/codecop.svg" alt="Picked by StillWorks" width="230" height="54"></a>